Picture this: a client forwards their insurer's cyber insurance proposal form. One question asks which recognized cyber security or information governance standards they comply with. Another asks for a control list. Your week was already full, and now you have to sound like a compliance department.
You don't need to chase a single mandated framework. The HIPAA Security Rule doesn't require one; it lets covered entities use any security measures that reasonably and appropriately implement its standards, based on their size and capabilities. And at least one insurer's form, Chubb's Cyber Enterprise Risk Management proposal in Australia, asks applicants in free text which recognized standards they comply with rather than naming one specific framework. Insurer acceptance varies by insurer and jurisdiction, so that approach won't hold everywhere, but it's a sign of how the question often gets asked. My view: pick a recognized framework that fits your clients and map its controls to settings you already run. That mapping is what you show on request, and it's what keeps a renewal from turning into a panic.
Your Client Just Asked for a Security Framework, What Do You Do?
A client's insurer or auditor wants to know which framework you follow. You don't need to invent a new one or chase a certification you don't have. You need to name a framework that's recognized and defensible, then prove you actually implement it.
Pick a Framework Your Insurer Won't Fight
How do you choose among NIST CSF, CIS Controls, or ISO 27001? The answer depends on your clients' regulatory context and what insurers and auditors in your region recognize.
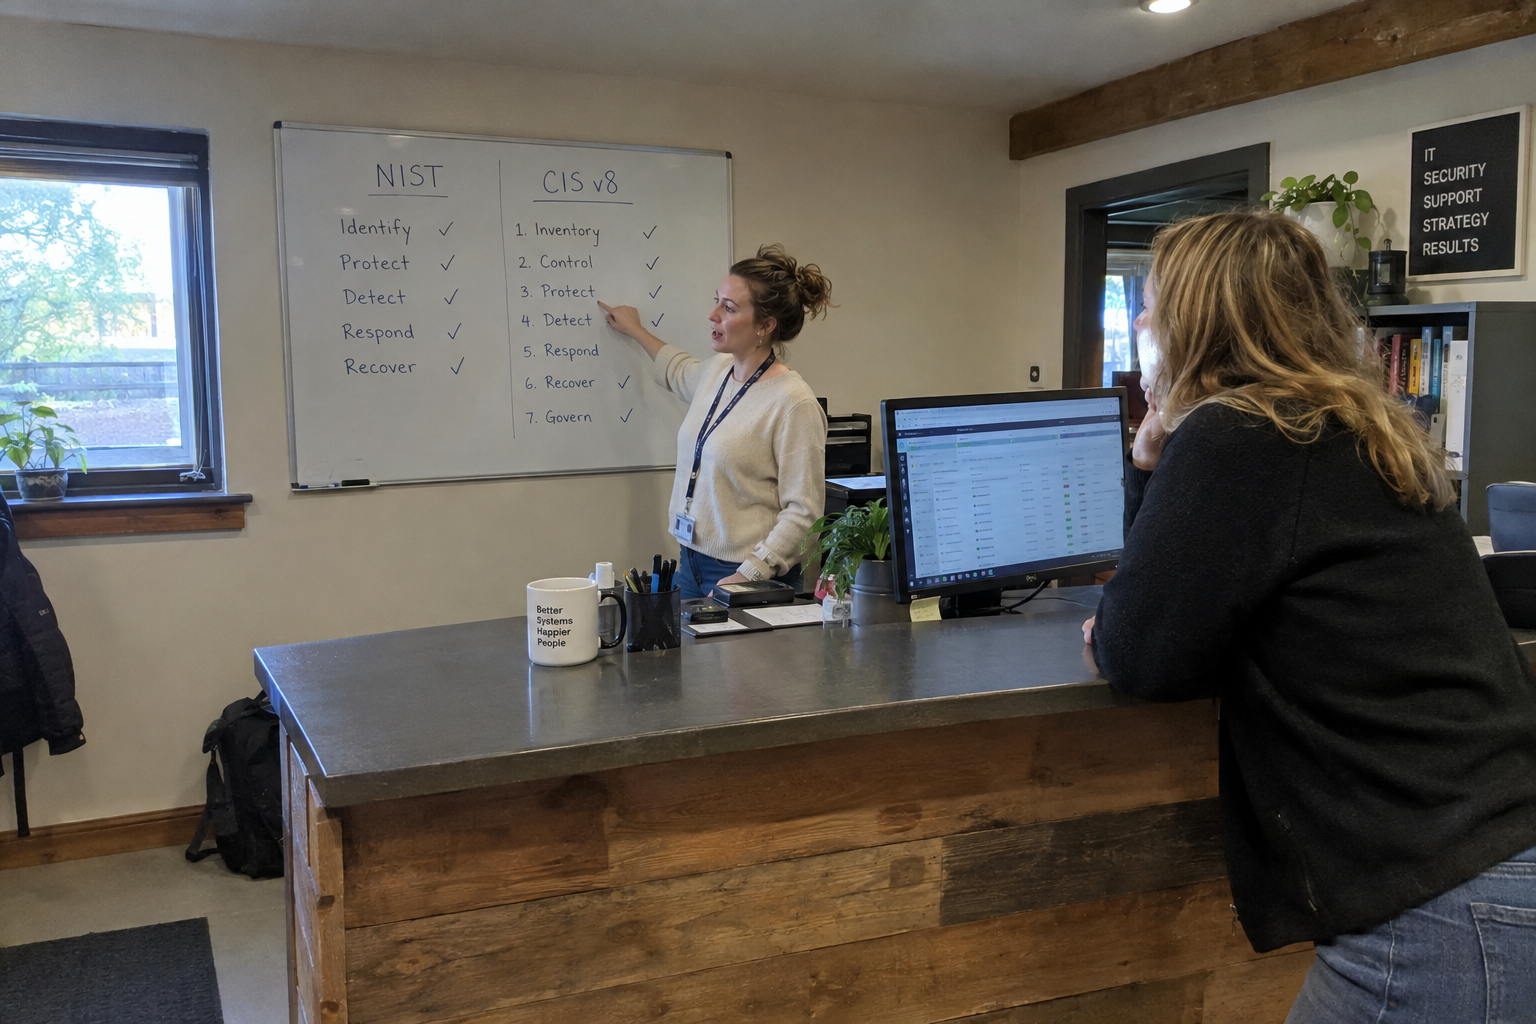
For most general business clients, I'd start with CIS Controls v8; it's lightweight and maps cleanly to common tools. For healthcare, the HIPAA Security Rule's flexibility means you can justify a NIST CSF mapping without a fight, since it explicitly allows any measures that reasonably implement its standards. Chubb's proposal form, as one example of an insurer's approach in one jurisdiction, lets you describe the standards you follow in free text. My view: start with NIST CSF or CIS Controls v8, and pick whichever your clients' auditors are more likely to have seen. If an insurer or contract names something else, deal with that separately.
Map Controls to Settings You Can Show on Request
What counts as evidence that you've implemented a control? For each framework control, list the technical setting you already run: a group policy, an EDR policy, an MFA configuration. Then keep a screenshot or config export as proof.
Say you run a dental client. For the NIST CSF access control control, you show the group policy that enforces least privilege on every endpoint. For the identity control, you show the MFA policy on their email tenant. That's a map: control, setting, proof.
The map is what you hand over when an auditor asks. It demonstrates due diligence, which is what most requests are really after. It doesn't guarantee insurance approval, but it gets you past the first round of questions.
Keep Evidence Current so a Renewal Takes an Afternoon
The part that actually breaks is maintenance. A one-time map goes stale the moment you change a tool or a policy. The fix is a recurring habit, not a project.
Set a quarterly review, plus an event-driven update whenever you change a tool or config. After a client adds EDR, update that client's endpoint protection control in the map. Name one owner, say an engineer or a part-time consultant, to keep the repository current. If that person is away, make sure a documented backup covers it.
Between changes, the quarterly check is enough. When the client changes insurers, re-check the map against the new insurer's form.
When One Framework Isn't Enough
What if a client's contract or insurer names a specific framework or certification? That's a separate requirement. You may need to supplement your chosen framework with additional controls, or pursue a certification like ISO 27001.
Say a client processes credit cards. You add the cardholder data controls on top of your NIST CSF map and keep them current, but you don't rebuild the whole framework around it.
This approach fails when a contract, regulator, or insurer names a specific standard or demands a certification. It also needs staff time; if you don't have a named owner for the evidence repository, the map decays and you're back to scrambling. One option is to bring in a security consultant to keep internal systems and client baselines in line, which one MSP did at roughly $5,000 a month when it didn't have the in-house hours. Treat that figure as an example to set against your own costs, not a benchmark.
Your Next Step: Start With One Client's Evidence Map
On Monday, pick one client. Choose a framework, NIST CSF or CIS Controls v8. List the two controls you already implement most cleanly, and map them to the settings you have. For a dental client, that's the MFA policy on their email tenant and the email filter settings.
That one map becomes your template. Once it exists, you can scale it across your client base within a quarter. The next renewal is a matter of pulling the current export and checking it against the map, not rebuilding the answer from scratch.
mspoutpost.com/articles/pick-a-security-framework-your-clients-insurers-will-actually-accept-2
Written by Dana Kowalski
MSP Outpost publishes information, not legal, financial, insurance, tax or compliance advice, and reading it creates no professional relationship. For decisions about your business, talk to a qualified professional.